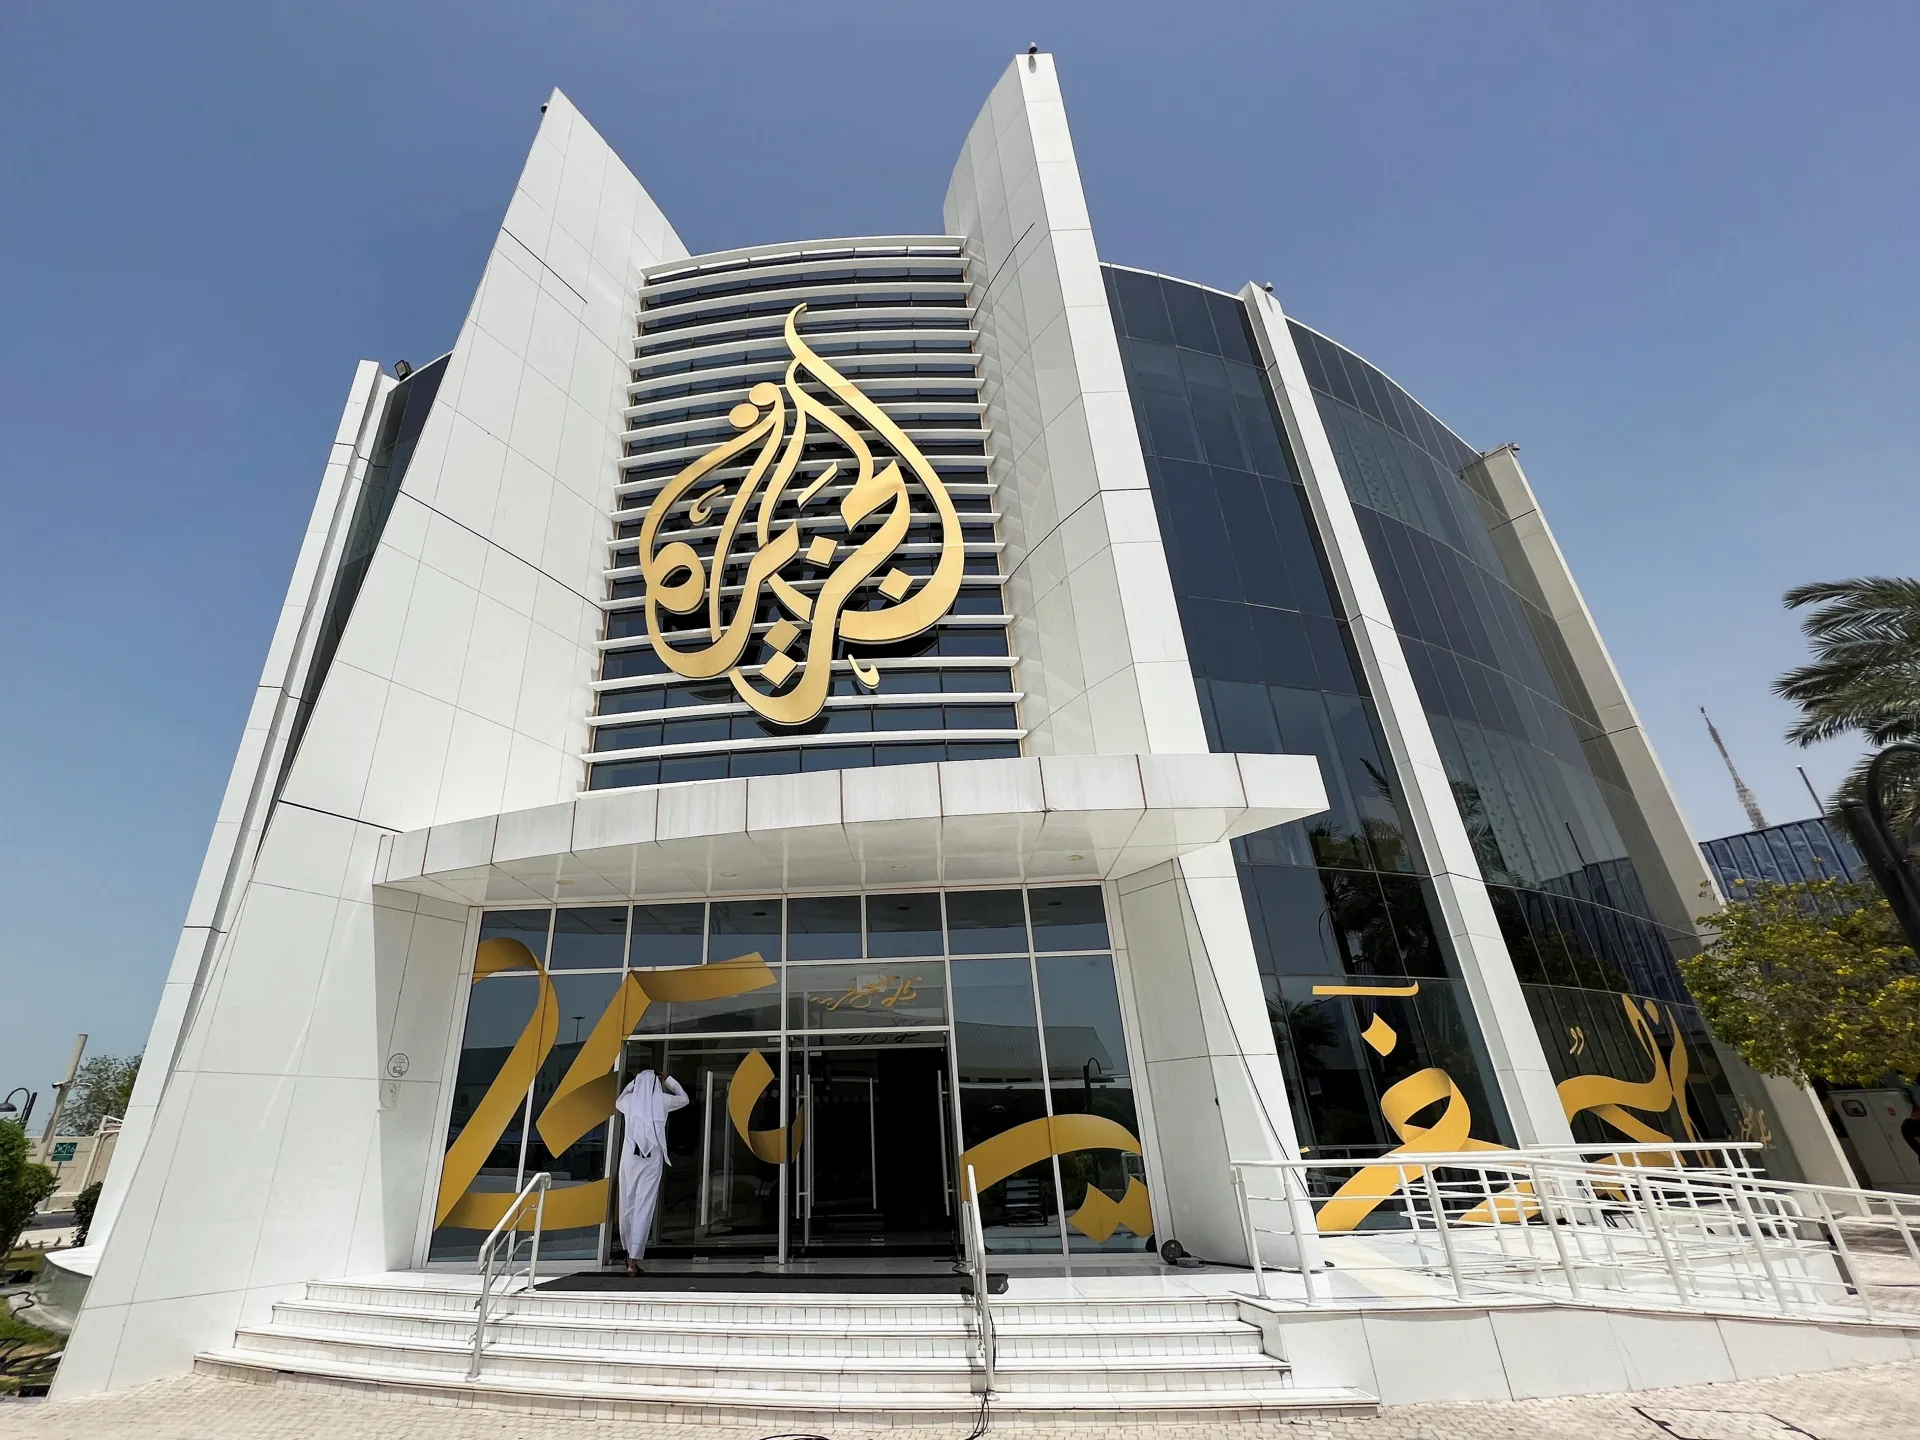
An investigation found that an Israeli ad-tech firm helped install spyware on devices used by Al Jazeera journalists and other organizations.
An Israeli advertising company named Discover-Tech helped install spyware on many devices. These devices belonged to Al Jazeera staff and other global organizations. A Citizen Lab investigation confirmed these findings this week.
Also, the Al Jazeera Media Network spoke out against the attacks. They believe targeting journalists hurts press freedom. The network plans to keep protecting its employees and computer systems.
Next, experts identified the software as a product of Candiru. The United States blacklisted this firm in 2021. It conducts malicious cyber activities against people around the world.
Researchers at the University of Toronto studied the attack methods. They found that Discover-Tech bought ads that contained hidden spyware. These ads redirected user devices to malicious software.
As a result, the spyware used a "zero-click" method. This means a device gets infected just by showing the ad. No user action is needed to start the spying process.
Meanwhile, Al Jazeera's tech team first noticed odd patterns in 2024. The strange activity lasted throughout 2025. They then asked Citizen Lab to investigate the issue further.
After that, the research team analyzed network logs from the network. They found a clear signature of the attacks. This evidence helped verify how the hackers operated.
Furthermore, a security firm in New York uncovered more details. Confiant reported that these ads reached sensitive networks. This included the Pentagon and the International Criminal Court.
Finally, Candiru's software has a long history of abuse. It has tracked at least 100 dissidents and reporters. These attacks happen in many different countries.